NIS2 & Compliance
An overview of requirements, and what they concretely mean for you
Organisations face many different requirements for information and cybersecurity. Some come from legislation, others from standards, contracts or frameworks the organisation itself has chosen to work by.
We help create an overview of the requirements relevant to you, assess how your existing practice measures up to them, and identify where further effort is needed.
NIS2
NIS2 sets requirements for, among other things, risk management, security measures, management responsibility and follow-up.
Many of the requirements can be found in ISO 27001/27002, so it makes sense to start with what you already have.
We help create an overview of what is in place, where the gaps are, and what should be prioritised.
Compliance
Compliance is not only about having policies and documentation, but about being able to show that the requirements are actually met in practice.
We help bring relevant requirements together in a common structure, reuse documentation and controls across requirements, and create a more complete picture of compliance.
From insight to concrete priorities
A structured approach that creates momentum
We turn external requirements and internal needs into a realistic, focused effort.
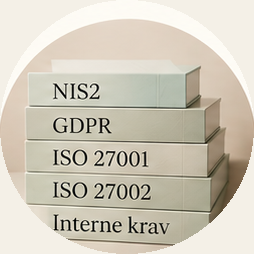
Where do you stand?
What does it mean for you?
What should you prioritise?
How do you move from plan to practice?
How do you stay on course?
Compliance Assessment
If you need a more systematic picture of compliance, Loft Insight offers an independent Compliance Assessment, where we look at documentation, implementation and actual practice.
See Compliance AssessmentCONTACT
Do you have questions about NIS2 or compliance?
We are happy to have an informal dialogue about your challenges.